
IP Spoofing Attack: Explained
Key Takeaways
- Hackers use IP spoofing to impersonate legitimate IP addresses, allowing unauthorized access to networks and sensitive data.
- Popular methods include DDoS attacks, Adversary-in-the-Middle attacks, and Masking Botnet attacks, which can result in serious security breaches.
- Digital certificates verify the identification of devices and users, ensuring secure communication and avoiding IP spoofing by identifying legitimate sources.
- Protect your organization by putting in place strong security measures like packet filtering and certificate-based security solutions.
One nasty strategy that needs our attention in the ever-changing environment of cybersecurity threats is IP spoofing. Given the increasing integration of the digital sphere into our everyday lives, it is important to comprehend the consequences of IP spoofing attacks.
Consider the case when a cybercriminal sets up a phony coffee shop with a free Wi-Fi sign to lure unwary customers into connecting to their network. This comparison highlights the seriousness of IP spoofing, a technique hackers use to impersonate authentic IP addresses to access networks without authorization to intercept and use private data.
This article explores:
- IP attacks
- IP spoofing
- IP spoofing prevention
What Is IP Address Spoofing?
The act of creating Internet Protocol (IP) packets with a malicious source IP address to mimic a different computer system is known as IP spoofing, also known as IP address spoofing.
IP spoofing gives attackers the ability to behave maliciously, frequently undetected. This might involve someone stealing your data, installing malware on your device, or bringing down your computer servers.
How Does IP Spoofing Work?
Let’s begin with some context.
- First, data is divided into several packets for transmission over Internet traffic.
- Each packet is then delivered separately and combined at the end.
- The source and destination IP addresses are among the details in every packet’s IP (Internet Protocol) header.
IP spoofing is when a hacker uses tools to change the source address in the packet header so that the receiving computer networks believe the incoming packets are from a reliable source and accept it, such as another computer on an authorized network.
Warning: As this occurs at the network level, there are no outward indications of manipulation.
The IP spoofing diagram, below, illustrates how IP spoofing works.
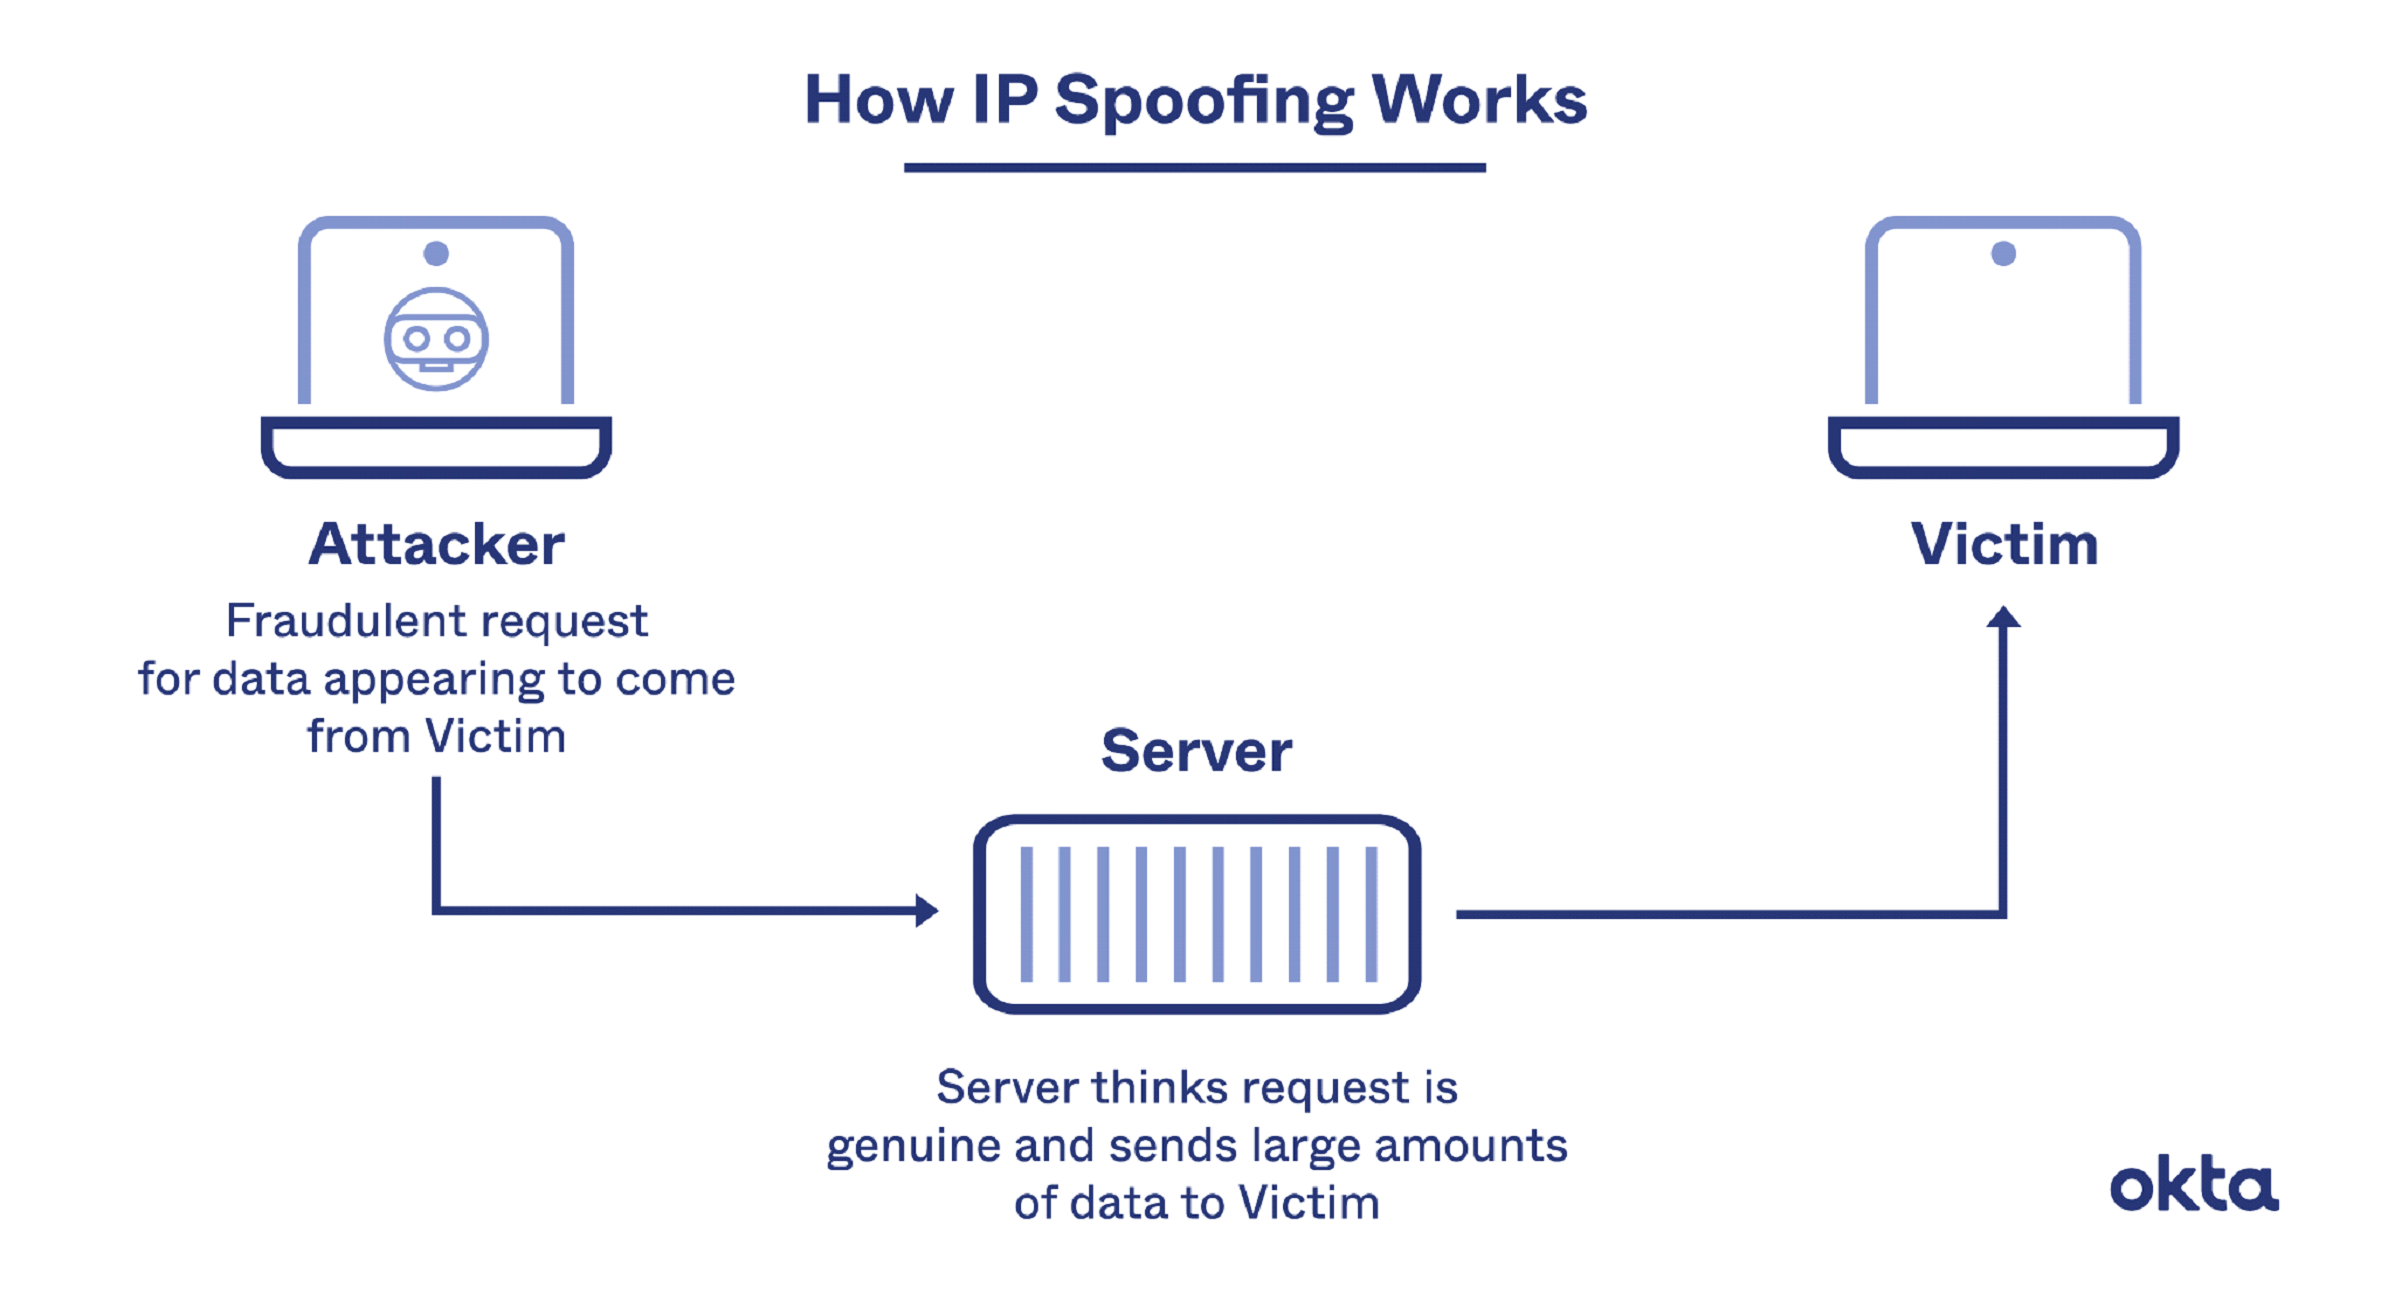
IP address spoofing can be used to get around IP address authentication in systems that depend on verifying IP addresses before trusting connections between networked computers.
Once a hacker breaches the network device and makes it inside, looking into the system is simple. Due to this weakness, advanced security techniques, such as multi-step authentication, are gradually replacing the usage of basic authentication as a defense method.
While IP spoofing is frequently used by hackers to commit online fraud and identity theft or to take down business websites and servers, it can also have legal applications.
For instance, businesses could utilize IP address spoofing to test websites before they go live. Testing the website and seeing whether it can withstand many logins without overloading would generate thousands of virtual users. Utilizing IP spoofing in this manner is not prohibited.
What Is the Impact of IP Spoofing?
The impact of IP spoofing can be severe, depending on the circumstances. Attackers can use IP spoofing to steal private data, install malware, or crash entire networks.
IP spoofing opens the door to serious attacks like:
- Distributed Denial of Service Attacks
- Adversary-in-the-Middle (also known as Man-in-the-Middle) Attacks
- Masking Botnet Attacks
All of these attacks can have serious long-term consequences, which is why it’s crucial to protect your network.
Types of IP Spoofing
Distributed Denial of Service (DDoS) Attacks
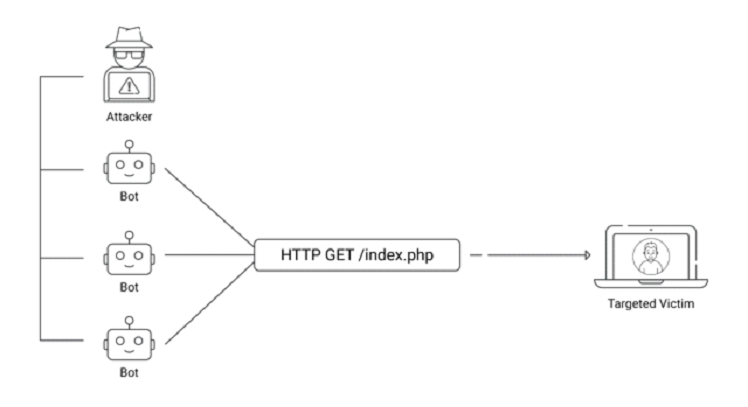
Hackers use fake IP addresses to flood computer systems with data packets during a denial-of-service attack. This enables them to remain anonymous while slowing down or crashing a network or website with high internet malicious traffic volumes.
The following flowchart illustrates how a DDoS attack works.
Masking Botnet Devices
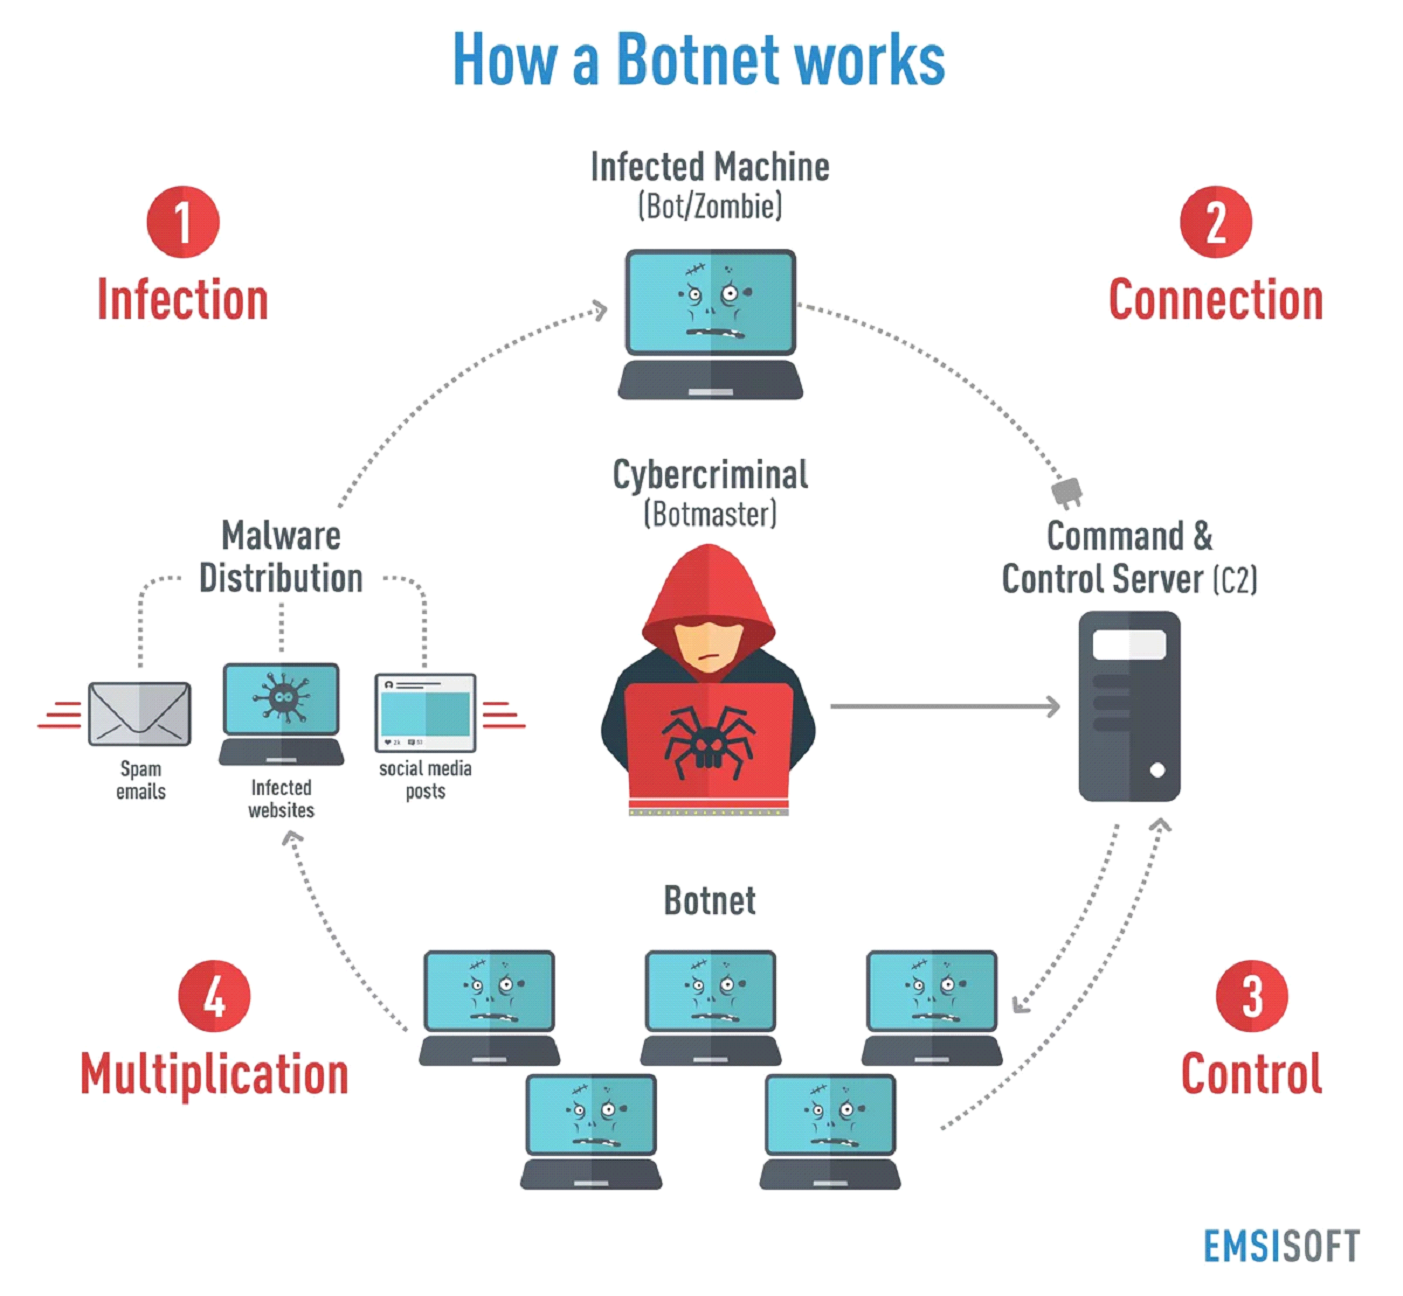
By masking botnets, IP spoofing may be used to gain access to machines. A botnet is a collection of computers that hackers may take control of from one central location. A specialized bot that operates on each machine performs fraudulent activities on the attacker’s behalf.
Because every bot in the network has a fake destination IP address, making the malicious actors difficult to identify, IP spoofing enables the attacker to conceal the botnet. This can extend an attack’s duration to increase its reward.
The following diagram shows how a botnet works.
Man-in-the-Middle Attacks
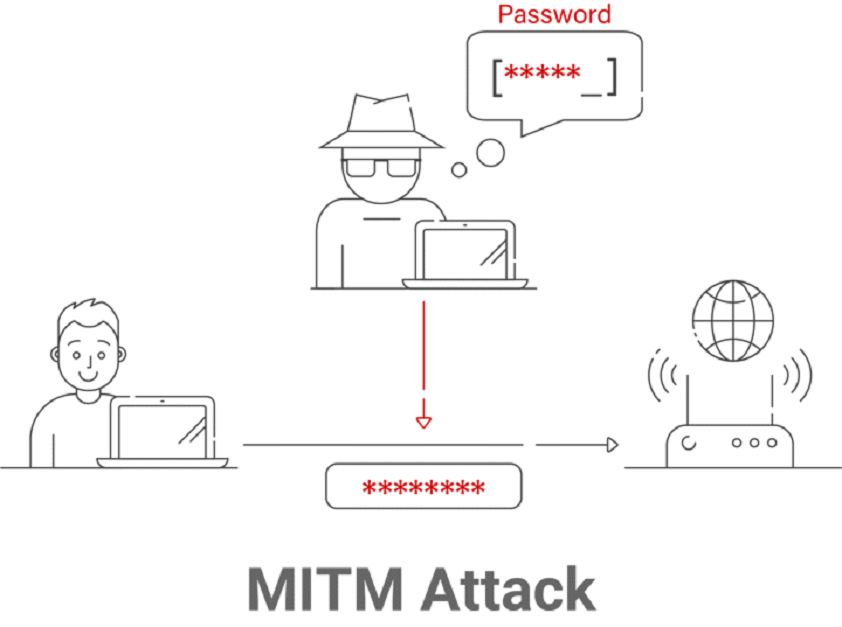
‘Man-in-the-Middle’ (MITM) attacks are another malicious type of IP spoofing that aims to stop two computers from communicating, change the packets, and send them again without the original sender or recipient noticing.
Attackers can follow every detail of a conversation if they manage to fake an IP address and get access to personal communication accounts. Data theft, user redirection to phony websites, and other activities are feasible from there.
MITM attacks can be more profitable than other types of hacking because, over time, hackers amass a plethora of sensitive data that they may exploit or sell.
The following diagram illustrates how MITM attacks work.
Examples of IP Spoofing
When attackers conduct a DDoS attack, they utilize fake IP addresses to overload computer network servers with fraudulent packet volumes too enormous for the destination computers to manage.
Botnets are frequently used to deliver packets that are distributed globally. Large botnets may comprise tens of thousands of machines, each of which may impersonate many source IP addresses at the same time. The automated attacks are difficult to track down.
Following are some examples of how spoofing has been utilized in DDoS attacks:
GitHub: GitHub was the target of what at the time was thought to be the largest DDoS attack ever on February 28, 2018. Attackers submitted requests to memcached servers, frequently used to speed up database-driven websites, by impersonating GitHub’s IP address.
A factor of around 50 magnified the data the servers provided from those calls to GitHub. Consequently, up to 51 kilobytes were delivered to the victim for every byte supplied by the attacker. A malicious traffic spike of 1.35 terabits per second knocked GitHub down for ten minutes.
Tsutomu Shimomura: Hacker Kevin Mitnick used IP spoofing to target rival hacker Tsutomu Shimomura’s systems on December 25, 1994. By discovering the pattern of TCP sequence numbers that the computer creates, Mitnick took advantage of the trust connection that existed between the server and Shimomura’s X terminal computer.
He sent an endless stream of SYN requests from fake IP addresses that were routable but inactive, flooding the system. The computer’s memory became full of SYN requests as it could not respond to the queries. We call this method SYN scanning.
How to Detect IP Spoofing
IP spoofing is difficult for end users to detect, which makes it risky. This is because Layer 3 of the Open Systems Interconnection communications architecture, or the network layers, is where IP spoof attacks are executed.
This eliminates any outward indications of manipulation, since fraudulent internet connection requests frequently seem authentic from the outside.
However, businesses may examine endpoint traffic using network monitoring software. The most popular technique for doing this is packet filtering.
Inconsistencies between a packet’s IP address and the required IP addresses listed on access control lists (ACLs) are detected by packet filtering systems, which are frequently found in routers and firewalls. Additionally, they identify false packets.
Ingress filtering and egress filtering are the two primary forms of packet filtering:
When a packet arrives, ingress filtering examines it to see if the source IP header corresponds to an allowed source address. Packets that appear suspicious will be refused.
Egress filtering scans outgoing packets for source IP addresses that differ from those on the company’s network. This is intended to stop insiders from using IP spoofing to conduct attacks.
What Are Other Types of Network Spoofing?
Spoofing comes in various forms, and it frequently occurs on IP-based networks. However, most do not involve changing a packet’s IP address, known as IP address spoofing.
Other forms of spoofing that work with IP addresses are as follows:
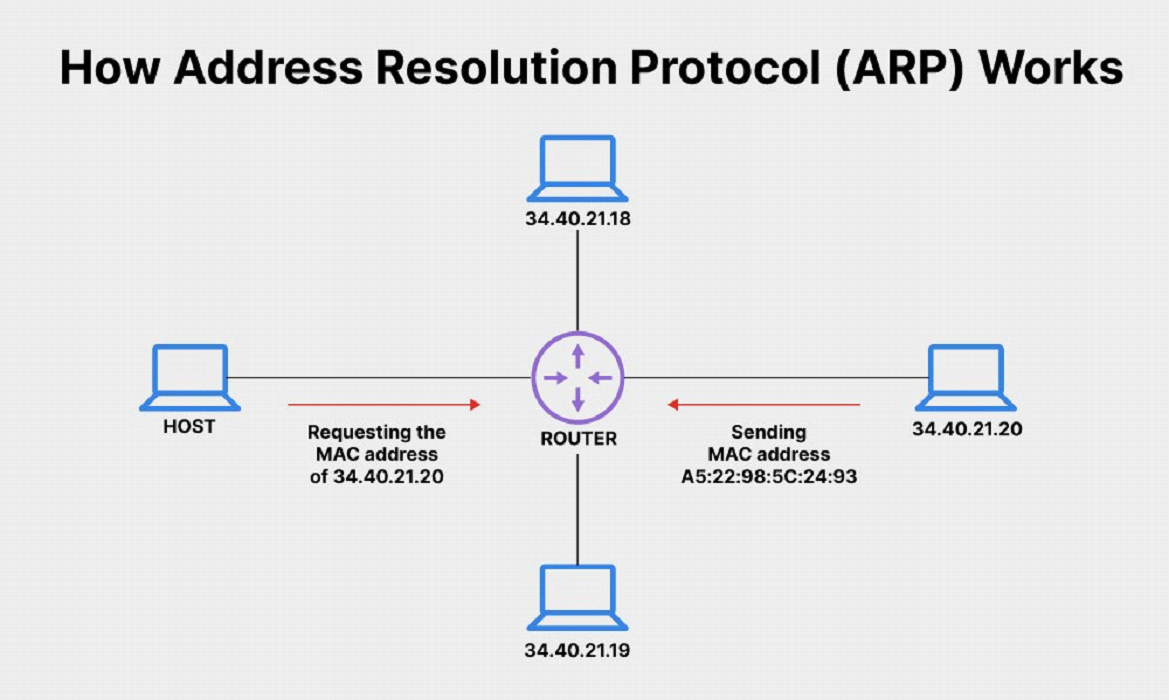
Address Resolution Protocol Spoofing
When an attacker uses a local area network (LAN) to transmit bogus ARP messages, it’s known as an ARP spoofing attack. This ties the attacker’s media access control address (MAC address) with the IP address of a genuine computer or server on the network. This happens in the Ethernet frames carrying that protocol at the data link layer.
The following image illustrates how ARP works.
Domain Name System (DNS) Spoofing
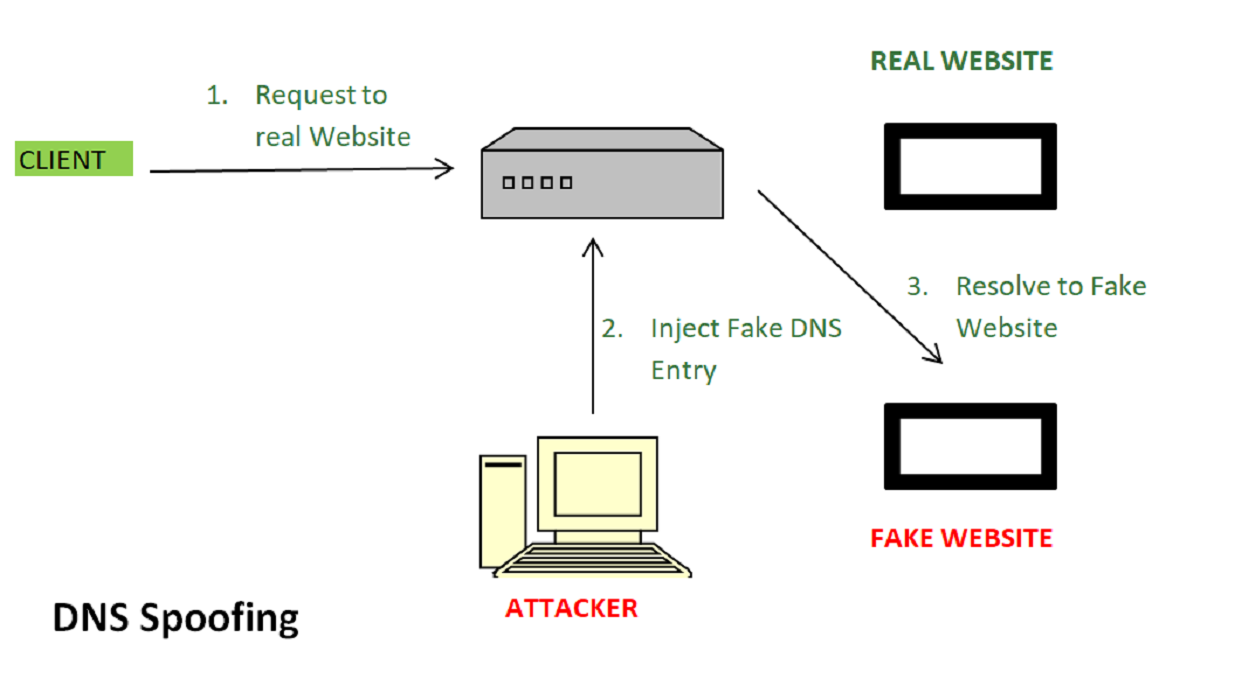
A DNS spoofing attack records and directs internet traffic toward phony servers rather than real ones. Webpages are mapped from IP addresses to DNS servers, which users access to access webpages.
A malicious actor can insert fictitious DNS entries into DNS servers, causing users to access the server and be routed to the hacker’s inserted site instead of their intended one, as illustrated in the graphic below.
Other spoofing techniques target various kinds of data and might not even remotely interfere with IP addresses. Here are a few instances:
Caller ID Spoofing
Caller ID spoofing modifies the caller ID to simulate a call originating from a different location. This frequently occurs when telemarketers dial the target’s area code.
Email Spoofing
Attackers tamper with email header data to make it appear that a different address sent the message. A phishing assault frequently includes a spoof email that links to a replica of a website that looks to be the original.
The fake website aims to deceive its intended audience into providing login credentials or other confidential data.
Global Positioning System (GPS) Spoofing
The act of deceiving a mobile device into displaying a position that differs from its actual geographic location is known as GPS spoofing. A third-party program that generates distinct location and navigational data can be used.
Short Message Service (SMS) Spoofing
SMS or text message spoofing is changing the sender’s phone number to hide their actual number. In their communications, attackers could include links that lead to malware downloads or phishing websites.
Using this technique, legitimate organizations may also create an easy-to-remember alphanumeric ID instead of a phone number that is hard to remember.
Uniform Resource Locator (URL) Spoofing
In this kind of spoofing, attackers utilize a nearly exact replica of a legitimate URL, just with a few characters altered.
The idea is to trick the victim into visiting an authentic webpage and then get them to submit sensitive data on it.
Are There Legitimate Use Cases for IP Spoofing?
Yes, there are. Although IP spoofing is often associated with cyberattacks, it also has legitimate uses.
For example, engineering teams use IP spoofing to test website performance; teams alter the source IP address in data packets to simulate heavy traffic loads.
Security teams also use IP spoofing to test the performance of firewalls and routers. By spoofing IP addresses, security teams can test whether perimeter controls are effectively filtering out unauthorized packets.
In most cases, though, IP spoofing attacks are malicious, and it’s crucial to protect your network against them.
How to Prevent Spoofing Attacks
You can stop spoofing attacks by using smart security tools.
For example, most phishing emails will not get through a spam filter or your mailbox. Several businesses use similar software and even certain network providers to prevent spam calls from getting to consumers’ phones.
Info: Software that detects spoofing attempts may offer more defense against certain spoofing types previously discussed, improving your capacity to identify and stop them before they can do any damage.
A few recommended practices might lessen the chance that you will become a target of a spoofing attack:
- Avoid relying on trust relationships for network authentication wherever feasible. If not, attackers may use those connections to pull off effective spoofing attacks.
- Use packet filtering to identify and reject packets with contradicting source address information.
- Deploy network protocols that use cryptography, such as Secure Shell (SSH) and HTTP Secure (HTTPS), to provide your environment with an extra degree of security.
Safeguard Your Digital Frontier with SecureW2
When it comes to understanding the complex world of cybersecurity, IP spoofing is one dark threat that requires our combined attention. Safeguarding our digital lives requires knowing IP spoofing and avoiding it, much like we would secure our houses against prospective intruders.
In this endeavor to achieve digital security, SecureW2 proves to be a reliable partner. Using state-of-the-art techniques like data encryption via certificates and 802.1X EAP-TLS authentication, SecureW2 significantly reduces the risk of IP spoofing by helping prevent devices and credentials from being compromised.
Schedule a free demo to learn more about how certificate-driven security can protect your organization’s devices and networks from compromise.
Frequently Asked Questions
What is IP spoofing with an example?
IP spoofing is a technique used to disguise the real source IP address in a network packet, often to “spoof,” or impersonate, a different device’s IP address.
For example, imagine that an attacker spoofs your IP address and, using that spoofed IP, sends a request to a public server, asking for large volumes of data. Your device is quickly overwhelmed with a mass of incoming data, making it inoperable.
Can IP spoofing be detected?
Yes, it’s possible to detect IP spoofing. Successful IP spoofing detection relies on perimeter defenses at the router and firewall level. Detection typically focuses on tracking the origin and behavior of incoming packets, which makes perimeter defenses crucial.
How does IP spoofing work?
IP spoofing works by altering a network packet’s IP address, often in order to impersonate another device. The attacker creates a malicious packet, enters a fraudulent address into the sender field, and then delivers the packet to the target.
